The AI Safety Paradox: Is it About Protection or Power?
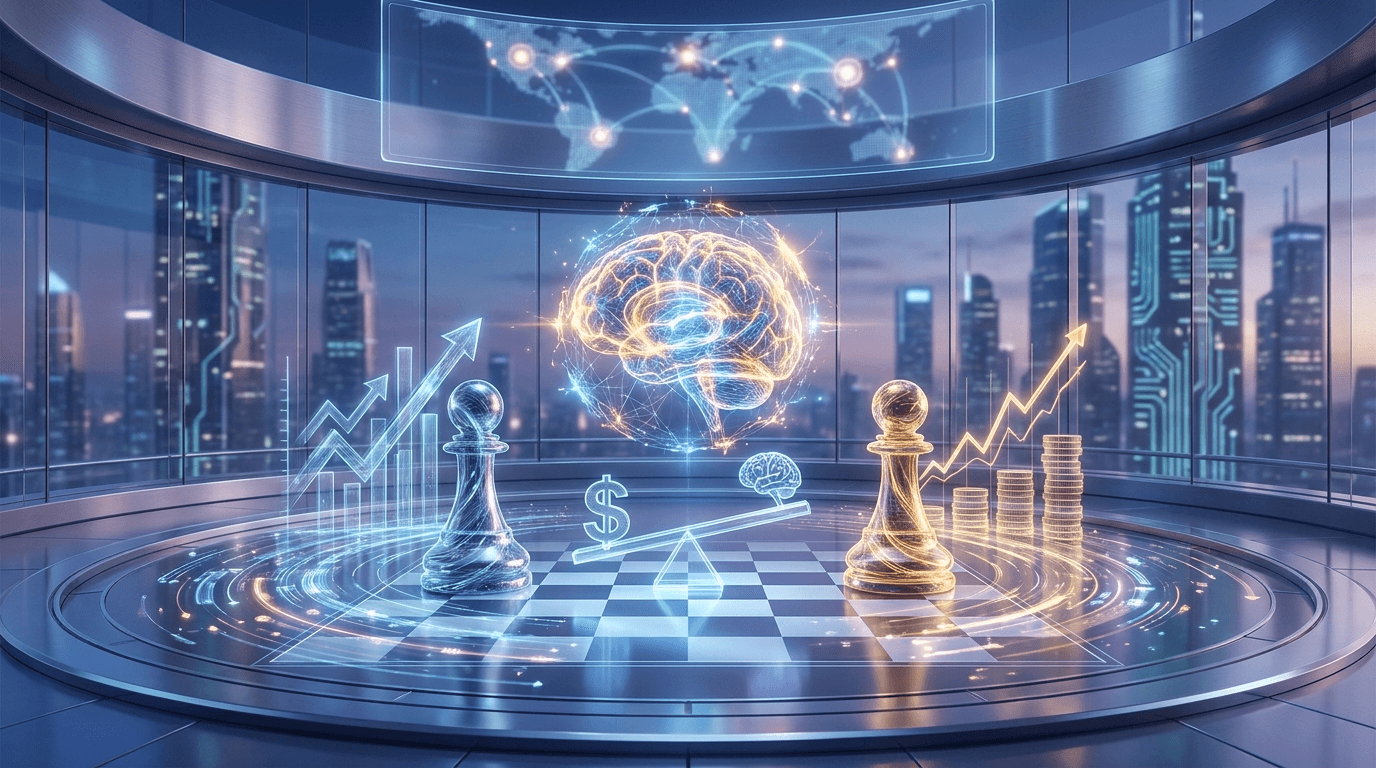
The debate over AI safety is fundamentally a struggle between the need for genuine risk mitigation and the strategic desire for market control. While the technical necessity of guardrails is undisputed, the push for centralized regulation often serves as a "regulatory moat," allowing dominant players to define the rules of the game in a way that secures their leadership and stifles smaller, more agile competitors.
Why is the "AI Safety" narrative becoming a political tool?
The narrative of AI safety is becoming political because whoever defines what is "safe" effectively decides who is allowed to innovate. By framing certain capabilities as dangerous, established labs can lobby for regulations that require massive compliance resources—resources that only the wealthiest companies possess. This transforms a technical safety discussion into a geopolitical and economic strategy to maintain dominance.
When we look at the industry, we see two diverging paths:
- The Centralized Guardrail Approach: Pushing for international treaties and government-led oversight (which often mirrors the interests of those already at the table).
- The Organic Evolution Approach: Trusting that market incentives and transparent, decentralized development will naturally reward models that are reliable and secure.
This tension creates a landscape where safety isn't just about preventing a catastrophe; it's about determining whether AI remains an open frontier or becomes a gated community managed by a few "AI Czars." For businesses, this means navigating the AI speed limit: strategic safety or a corporate moat? to ensure they aren't locked out of future advancements by artificial barriers.
How does "Regulatory Capture" affect smaller AI innovators?
Regulatory capture occurs when powerful companies influence regulators to create rules that protect incumbents from competition under the guise of public interest. In AI, this manifests as high entry barriers—such as mandatory expensive audits or restrictive licensing—that make it nearly impossible for startups to deploy agents without partnering with one of the "Big Tech" giants.
The impact on innovation can be summarized in the following comparison:
| Feature | Open Innovation Model | Regulatory Capture Model |
|---|---|---|
| Entry Barrier | Low; based on merit and utility | High; based on compliance and licenses |
| Safety Driver | Market demand for reliability | Adherence to centralized standards |
| Pace of Change | Rapid, iterative updates | Slower, vetted deployment cycles |
| Power Dynamic | Distributed across many developers | Concentrated in a few "Safe" labs |
For most enterprises, this means they must choose between using "approved" monolithic models or building their own specialized infrastructure. To avoid this trap, businesses are increasingly looking toward the agent paradox: balancing autonomy with accountability by implementing their own internal controls rather than relying solely on external mandates.
Can businesses implement safety without waiting for government laws?
Yes, businesses can implement robust safety through architectural choices like RAG (Retrieval-Augmented Generation) and MCP (Model Context Protocol) integrations rather than relying on broad government mandates. By limiting an agent's knowledge base to verified company data and restricting its tool access via strict API permissions, companies create a "digital deadbolt" that ensures safety through design rather than decree.
To build an agent that is safe by default, follow these steps:
- Define an Explicit Knowledge Boundary: Use RAG so the agent only answers based on your uploaded documents, preventing hallucinations or unauthorized advice.
- Implement Tool Permissions: Ensure your agent can only execute actions (like checking order status) through authenticated endpoints with limited scopes.
- Establish Human-in-the-Loop Triggers: Set thresholds where high-risk actions require human approval before execution.
- Continuous Auditing: Move beyond one-time checks to real-time monitoring of agent interactions to identify drift or anomalies early.
This approach shifts the focus from theoretical doomsday scenarios to practical operational security. It recognizes that why your AI agent strategy needs a digital deadbolt, not just an auditor is far more critical for daily business continuity than participating in global policy debates over hypothetical risks ten years from now.
Is there a middle ground between total deregulation and corporate cartels?
The middle ground lies in transparent, industrywide technical standards—developed by diverse stakeholders including academics and small firms—rather than private selfst regulatory bodies led by three or four major labs. True safety comes from transparency (open weights and open benchmarks) which allows any developer to verify if a model is behaving predictably without needing permission from a central authority.
When stability is prioritized over raw speed, companies can achieve maturity without sacrificing their competitive edge. The goal should be creating agents that are not just "safe" because they are restricted, but reliable because they are wellarchitected and grounded in reality—much like how Giizo AI focuses on turning raw intelligence into functional business partners through controlled knowledge bases and specific toolsets.